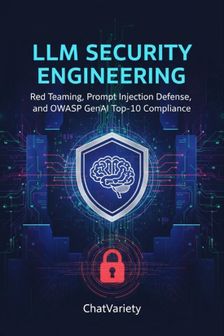
LLM Libri GmbH AI Security & Quantum-Safe Engineering- LLM Security Engineering

LLM Libri GmbH AI Security & Quantum-Safe Engineering- LLM Security Engineering

Tous les 2 prix et vendeurs

Hot Deal Alert – Meilleur prix !
Amazon.be· Vendeur reconnu
€ 9,11
3 à 4 joursLivraison gratuite
Check de website voor de levertijd | Gratis bezorgd > €20,-
Voir le produit
Voir le produit
Amazon.be Marketplace· Marketplace
€ 9,11
3 à 4 joursLivraison gratuite
Check de website voor de levertijd | Gratis bezorgd > €20,-
Voir le produit
Voir le produit

Spécifications

Belangrijkste kenmerken
EAN
9798198169647

Description du produit

Secure Your Enterprise AI Systems Before Attackers DoLarge language models are revolutionizing enterprise workflows, but they introduce an entirely new attack surface. LLM Security Engineering is the definitive, hands-on playbook for security engineers and AI developers looking to safeguard production AI applications.Go beyond abstract safety theory and master the concrete, tactical defenses required to protect against prompt injection, data exfiltration, supply chain poisoning, and autonomous agent exploits. This comprehensive guide maps directly to the latest OWASP GenAI Top-10 and Agentic AI Top-10 frameworks, providing you with the exact strategies needed for enterprise-grade compliance.What You Will Learn- Master Advanced Red Teaming: Execute structured attacks against LLM systems using industry-standard tools like promptfoo and Garak.- Defeat Prompt Injection: Detect and block direct and indirect prompt injection across the application, retrieval (RAG), and infrastructure layers.- Harden Autonomous Agents: Secure tool-use chains, multi-agent orchestrations, and mitigate downstream injection vulnerabilities.- Protect Intellectual Property: Defend against model extraction attacks and secure your AI supply chain, including models and fine-tuning datasets.- Build an Enterprise Security Program: Design an AI security lifecycle from risk assessment and continuous monitoring to specialized incident response playbooks.Whether you are securing a single customer-facing chatbot or orchestrating a complex fleet of autonomous AI agents, this book provides the adversarial mindset and engineering controls you need. Stop reacting to emerging threats and start engineering secure-by-design LLM applications today.

Avis

Aucun avis n’a encore été écrit

Tu possèdes ce produit et tu aimerais donner ton avis ? Commence ci-dessous à écrire ton avis. Selon le niveau de détail, écrire un avis prend en moyenne entre 3 et 10 minutes. Avec ton opinion, tu aides les autres visiteurs à faire un meilleur choix et tu tentes chaque mois de gagner 250 € ! Clique ici pour les conditions de l’action.

Quelle note donnes-tu à ce produit ?