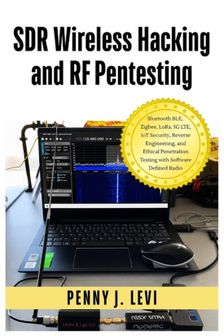
SDR Libri GmbH The Complete SDR & RF Engineering: SDR Wireless Hacking and RF Pentesting

SDR Libri GmbH The Complete SDR & RF Engineering: SDR Wireless Hacking and RF Pentesting

Tous les 2 prix et vendeurs

Hot Deal Alert – Meilleur prix !
Amazon.be· Vendeur reconnu
€ 27,87
3 à 4 joursLivraison gratuite
Check de website voor de levertijd | Gratis bezorgd > €20,-
Voir le produit
Voir le produit
Amazon.be Marketplace· Marketplace
€ 27,87
3 à 4 joursLivraison gratuite
Check de website voor de levertijd | Gratis bezorgd > €20,-
Voir le produit
Voir le produit

Spécifications

Belangrijkste kenmerken
EAN
9798193493389

Description du produit

Your smart lock broadcasts its presence to anyone listening. Your car key transmits the same secret every time you press unlock. Your phone trusts any cell tower strong enough to shout back. And right now, someone with a $20 radio and the right knowledge could be sitting in a parking lot, capturing it all.
While cybersecurity teams obsess over networks and endpoints, the most overlooked attack surface is literally floating through the air around us. SDR Wireless Hacking and RF Pentesting is the definitive field manual for seeing, capturing, and ethically exploiting the invisible radio frequency signals that power the modern world.
Inside this hands-on guide, you will learn how to: - Build a legal RF security lab and master the professional toolkit: HackRF, USRP, RTL-SDR, GNU Radio, and Universal Radio Hacker- Reverse engineer unknown protocols, capture proprietary remotes, and clone signals that most engineers assume are secure- Sniff, spoof, and break Bluetooth BLE pairing to compromise smart locks, fitness trackers, and medical implants- Exploit Zigbee, Z-Wave, and LoRaWAN networks - extracting network keys, injecting forged commands, and mapping entire smart homes from the sidewalk- Scan LTE and 5G cells, detect rogue IMSI catchers, and analyze cellular baseband vulnerabilities- Hack automotive RF: crack rolling-code key fobs, spoof tire pressure sensors, and execute relay attacks against passive entry systems- Fingerprint drone control links, hijack command channels, and spoof GPS/GNSS signals to misdirect navigation- Navigate FCC and international regulations, conduct responsible disclosure, and deploy defensive RF monitoring systems that catch attackers before they strikeWhether you are a penetration tester expanding into physical wireless security, a red teamer hunting attack vectors no firewall can stop, or a cybersecurity professional who refuses to let the airwaves remain a blind spot, this book gives you the technical depth and legal framework to operate at the cutting edge of RF research.
>Grab your copy now and claim your seat at the frontier of wireless security.

Avis

Aucun avis n’a encore été écrit

Tu possèdes ce produit et tu aimerais donner ton avis ? Commence ci-dessous à écrire ton avis. Selon le niveau de détail, écrire un avis prend en moyenne entre 3 et 10 minutes. Avec ton opinion, tu aides les autres visiteurs à faire un meilleur choix et tu tentes chaque mois de gagner 250 € ! Clique ici pour les conditions de l’action.

Quelle note donnes-tu à ce produit ?