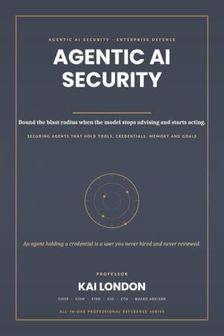
Libri GmbH Agentic AI Security All-in-One : Le manuel d'entreprise définitif pour sécuriser les agents IA autonomes, LLM, MCP, RAG, Tool Calling, système multi-agents

Libri GmbH Agentic AI Security All-in-One : Le manuel d'entreprise définitif pour sécuriser les agents IA autonomes, LLM, MCP, RAG, Tool Calling, système multi-agents

Tous les 2 prix et vendeurs

Choix le plus populaire
Prix le plus bas
Amazon.be· Vendeur reconnu
€ 161,58
6 jours ou plusLivraison gratuite
Check de website voor de levertijd | Gratis bezorgd > €20,-
Voir le produit
Voir le produit
Prix le plus bas
Amazon.be Marketplace· Marketplace
€ 161,58
6 jours ou plusLivraison gratuite
Check de website voor de levertijd | Gratis bezorgd > €20,-
Voir
Voir le produit

Spécifications

Belangrijkste kenmerken
EAN
9798182825382

Description du produit

Agentic AI Security All-in-One is an 825-page enterprise handbook for securing autonomous AI agents, LLMs, MCP, RAG, tool calling, multi-agent systems, identity, zero trust, red teaming, governance and AI cyber defence. Built around the Agent Containment Loop, it addresses the moment AI moves from answering to acting, when a model is given tools, credentials and permission to change the world on your behalf.Part I moves from answering to acting, states the threat model in precise terms and sets out the standards and authorities that govern it. Part II covers discovery and inventory: the agent bill of materials, finding every agent through runtime, repository and shadow discovery, classifying what you found by exposure, and third parties, SaaS agents and the MCP supply chain. Part III addresses prioritisation and programme design, including governance, ownership, the obligation register, wave planning and sequencing.Later parts go deep on agent identity and least privilege, tool-calling and MCP controls, RAG and retrieval security, containment, monitoring and kill switches for autonomous behaviour, multi-agent trust, red teaming agents, and the evidence, assurance and governance needed to run agents in regulated enterprises.Written for security architects, AI platform engineers, identity and access specialists, SOC leaders, red teamers, CISOs, risk and compliance professionals and technology leaders deploying AI agents in production. Part of the Understand, Architect, Attack, Defend, Govern series of enterprise AI security references.Key topics include: agentic AI security; autonomous agents; agent bill of materials; MCP and tool-calling security; RAG security; agent identity and privilege; zero trust for AI; multi-agent systems; containment and kill switches; AI red teaming; AI governance; AI cyber defence.

Aucun avis n’a encore été écrit

Question 1 sur 4

Tu possèdes ce produit et tu aimerais donner ton avis ? Commence ci-dessous à écrire ton avis. Selon le niveau de détail, écrire un avis prend en moyenne entre 3 et 10 minutes. Avec ton opinion, tu aides les autres visiteurs à faire un meilleur choix et tu tentes chaque mois de gagner 250 € ! Clique ici pour les conditions de l’action.

Quelle note donnes-tu à ce produit ?